Pre-Issuance Review
Independent challenge of draft findings, conclusions, recommendations, evidence and report logic before the report leaves the organization.
Independent review of audit evidence, workpapers, findings, recommendations and draft reports — before issuance, peer review or external scrutiny.
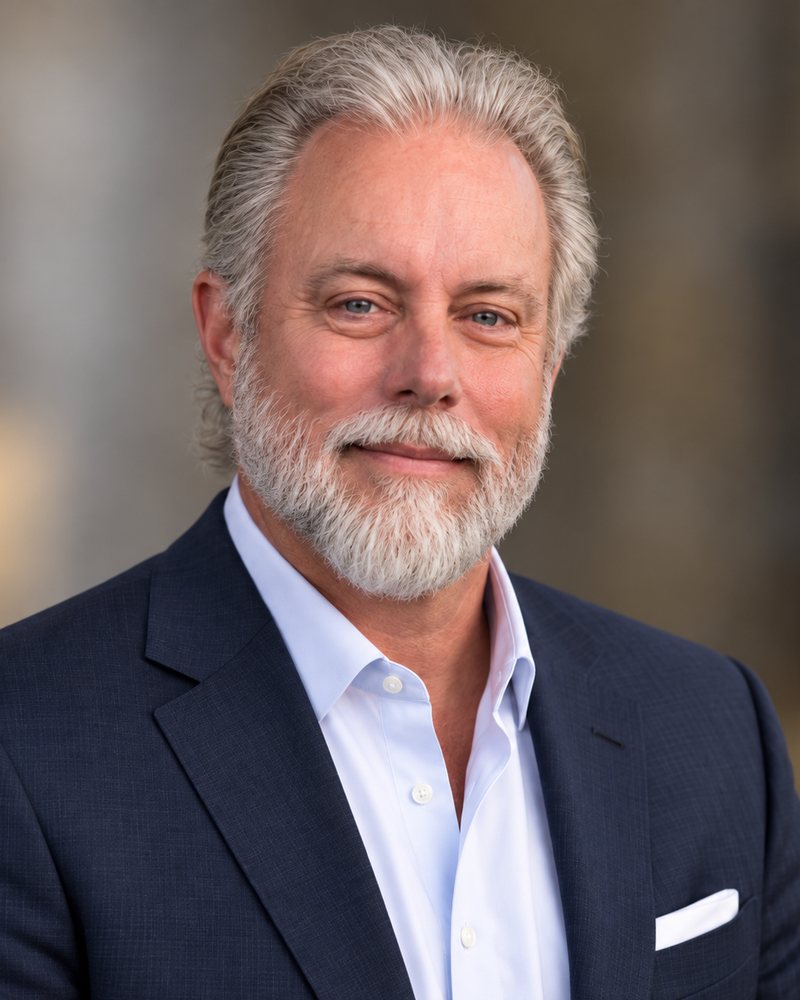
Principal-led by Bret D. Hunter, CIA, with 34 years of Federal Inspector General audit experience. Hunter Audit Services does not issue CPA attest opinions or external peer-review ratings.
An engagement team knows its work better than anyone. That familiarity can also make assumptions, unsupported inferences and documentation gaps harder to see.
Independent quality review asks a different question: if an experienced auditor had no investment in the conclusion, would the evidence lead that reviewer to the same place?
The objective is not to rewrite the team's audit. It is to identify the issues most likely to weaken defensibility, clarity or compliance while there is still time to correct them.
Do the workpapers actually support the finding and conclusion, including evidence that points the other way?
Can a reviewer move cleanly from criteria to condition, cause, effect, conclusion and recommendation?
Challenge comes from outside the engagement team, without a need to defend sunk time or prior decisions.
Independent challenge of draft findings, conclusions, recommendations, evidence and report logic before the report leaves the organization.
Focused review of whether documentation is sufficient, appropriate, internally consistent and capable of supporting the conclusions drawn.
Second-opinion review when a finding is disputed, unusually significant, sensitive or difficult to defend.
Independent monitoring or inspection support for organizations operating a GAGAS system of quality management.
Targeted review of selected engagements, documentation and quality practices before an external peer review or comparable assessment.
Rapid senior review of scope, evidence, methodology, workpapers or reporting when an engagement has stalled or confidence has dropped.
The 2024 Yellow Book shifted the framework from quality control to a risk-based system of quality management, with expanded monitoring and remediation requirements.
GAO specifically states that an audit organization may use a service provider, including another audit organization, to monitor or assist in monitoring its system of quality management.
For most audit organizations, the system was required to be designed and implemented by December 15, 2025, with the initial evaluation completed by December 15, 2026.
Monitoring is part of the organization's own quality-management system. This service does not represent itself as the organization's external peer review.
Potential conflicts, prior involvement and threats to objectivity are considered before accepting a review.
Whether the work performed actually addresses the audit objective and the material risks within scope.
Whether criteria are authoritative and testing is appropriately designed and executed.
Whether evidence is relevant, reliable and sufficient for the conclusion being drawn.
Whether evidence inconsistent with the emerging narrative was recognized and resolved rather than ignored.
Whether condition, cause, effect, conclusion and recommendation connect without unsupported inferential jumps.
Whether a knowledgeable independent reader can reproduce the logic of the report from the documented evidence.
Scope determines the format, but the output is normally a concise issues memorandum or review log prioritized by significance, with direct references to the work reviewed and a debrief with engagement leadership when useful.
Could materially undermine the conclusion, report defensibility, independence or compliance.
Should be resolved before issuance or external review but does not necessarily invalidate the engagement.
Improves clarity, traceability or efficiency without changing the substantive conclusion.
Hunter Audit Services is led by Bret D. Hunter, CIA, a former Senior IT Auditor with the Treasury Inspector General for Tax Administration.
His background includes 34 years in the Federal Inspector General audit environment, extensive cybersecurity and technology audit experience, and substantial experience reviewing audit evidence, workpapers, findings and reports.
That experience is particularly relevant to performance audits, IT and cybersecurity audits, FISMA-related work and other engagements conducted in government or government-contractor environments.